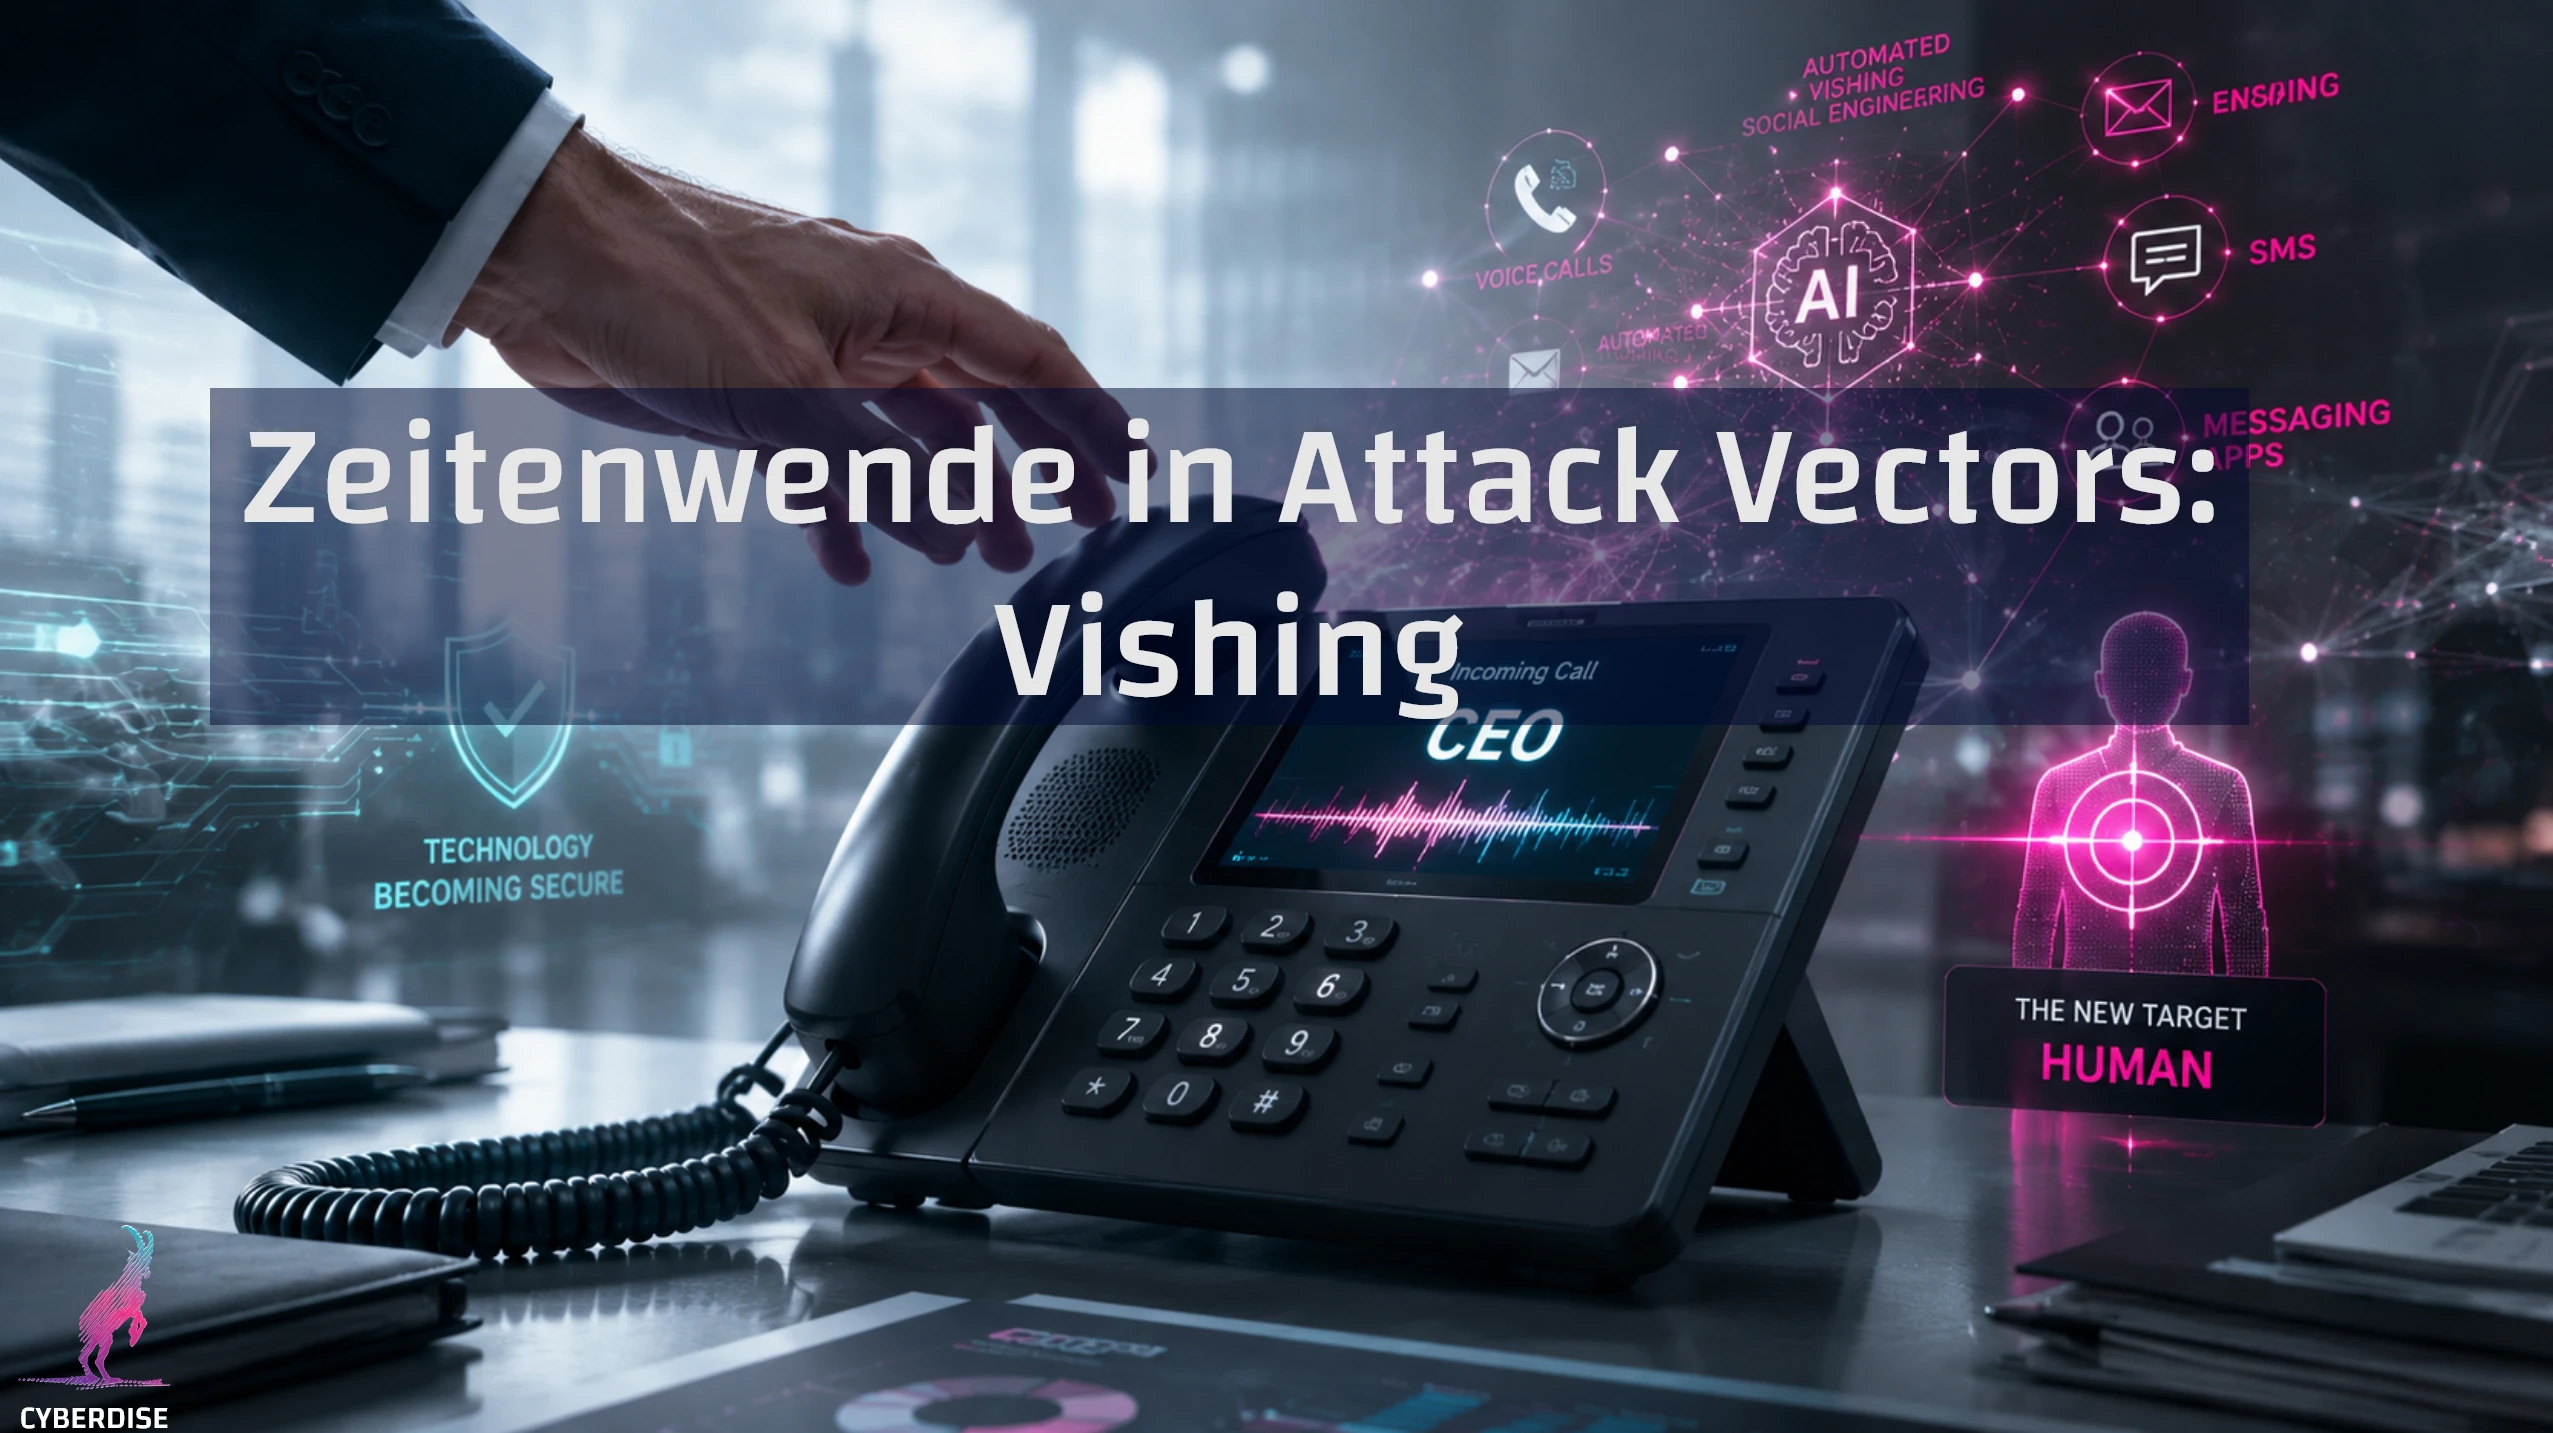
Picture this: your phone rings. The display shows your CEO’s name. When you pick up, you hear her exact voice, clear and crisp. She’s at the airport, in a hurry, and asks you to approve a multi-factor authentication (MFA) prompt right now so she can log in to an urgent board meeting.
Would your employees comply? In most organizations, the honest answer is: “Maybe” (read: yes). This is exactly the reaction a realistic vishing simulation makes visible — before a real attacker does.
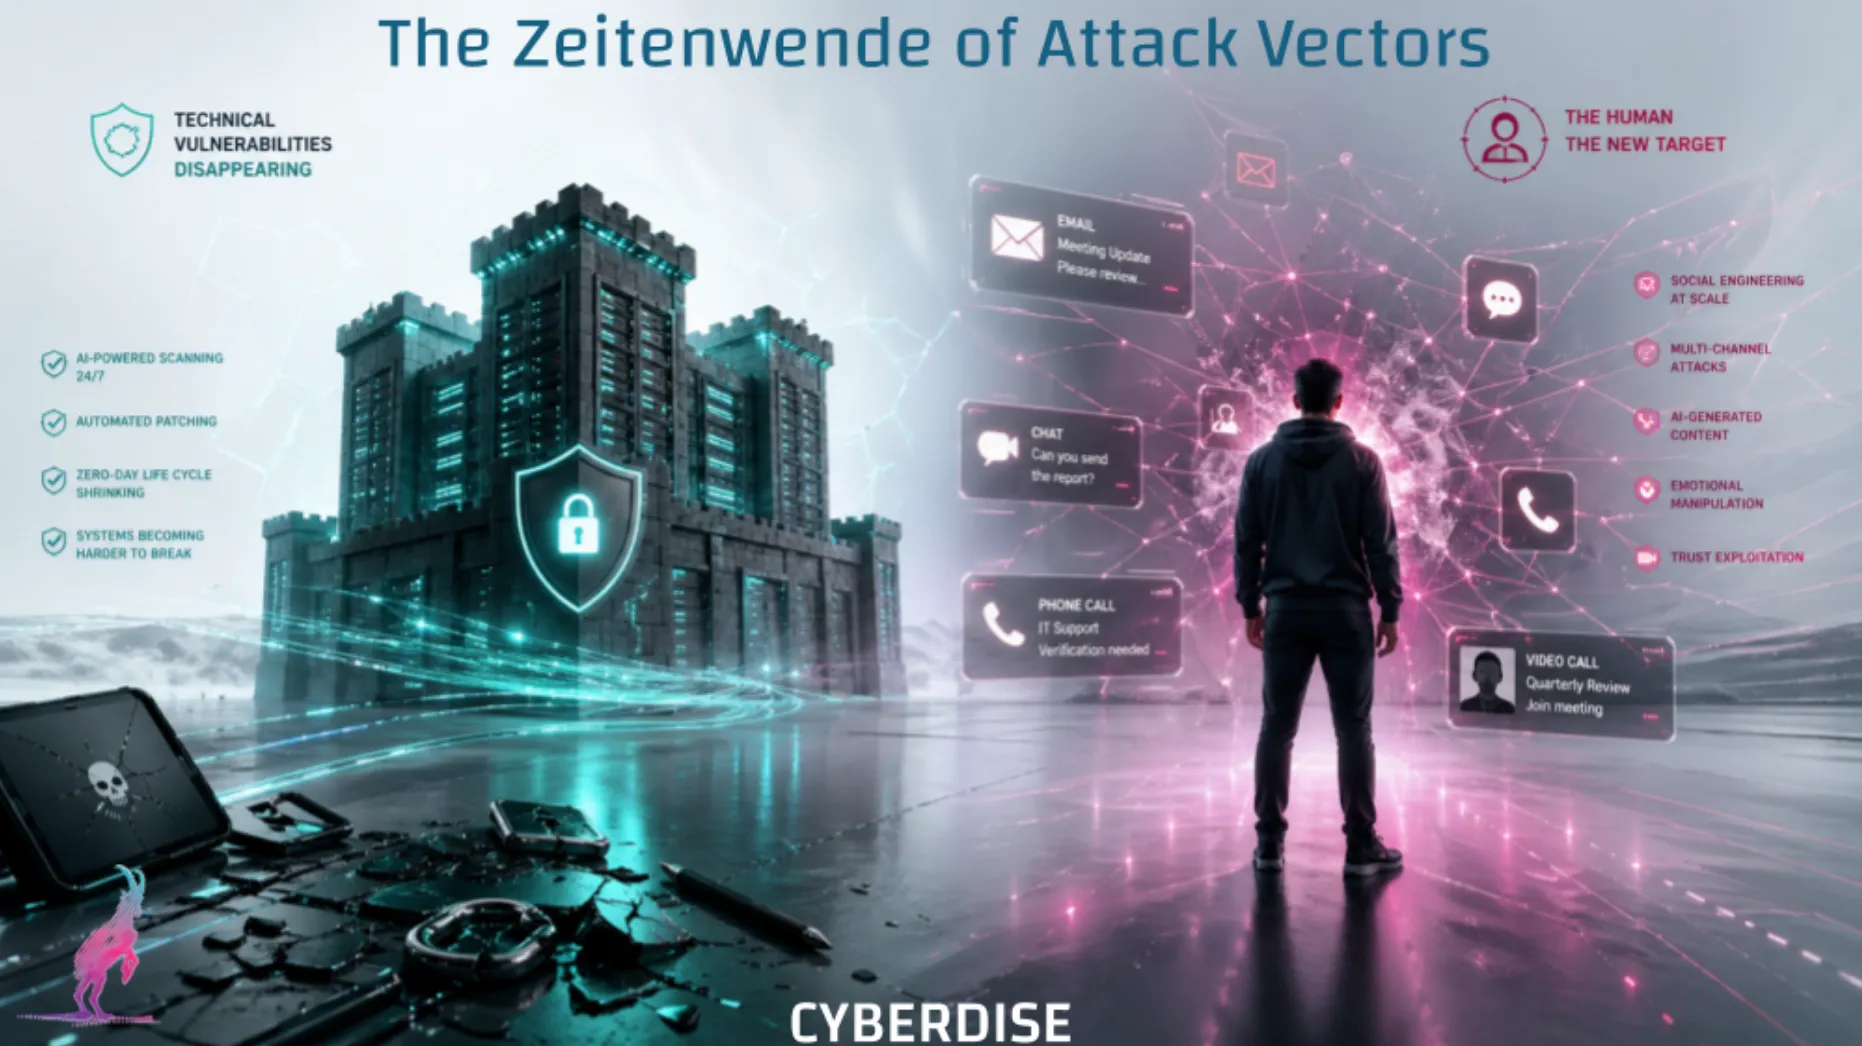
At Cyberdise, we often talk about how leadership and culture shape cybersecurity. Yet even the strongest security culture faces a massive paradigm shift. Attackers no longer hide only behind text-based emails; they call your team directly, armed with AI-powered voice clones that are indistinguishable from trusted managers or partners.
This is vishing (voice phishing). To counter this psychologically potent threat, we have to bring the defense directly to the phone lines.
The blind spot in modern awareness training
For years, cybersecurity training focused heavily on the inbox. Companies simulated phishing emails and (hopefully) taught colleagues to spot suspicious URLs.
But while technical filters have become excellent at catching most spam, they can’t scan a live conversation in real time the same way. Attackers know this. They deliberately exploit human factors like authority, urgency and trust. On top of that, attacks now combine several channels: imagine an SMS from the CEO arriving 15 minutes before the vishing call — “Calling you shortly, need your help.”
When psychological pressure is then applied on the phone, theoretical knowledge often isn’t enough. Employees need behavioral resilience. They have to know how to verify callers safely, without letting panic take over.
Realistic vishing simulations as a learning method
To train these scenarios safely, modern simulation modules recreate exactly these high-pressure situations. It’s not just about whether someone picks up, but how the interaction unfolds. An effective risk-prevention system is defined by the following:
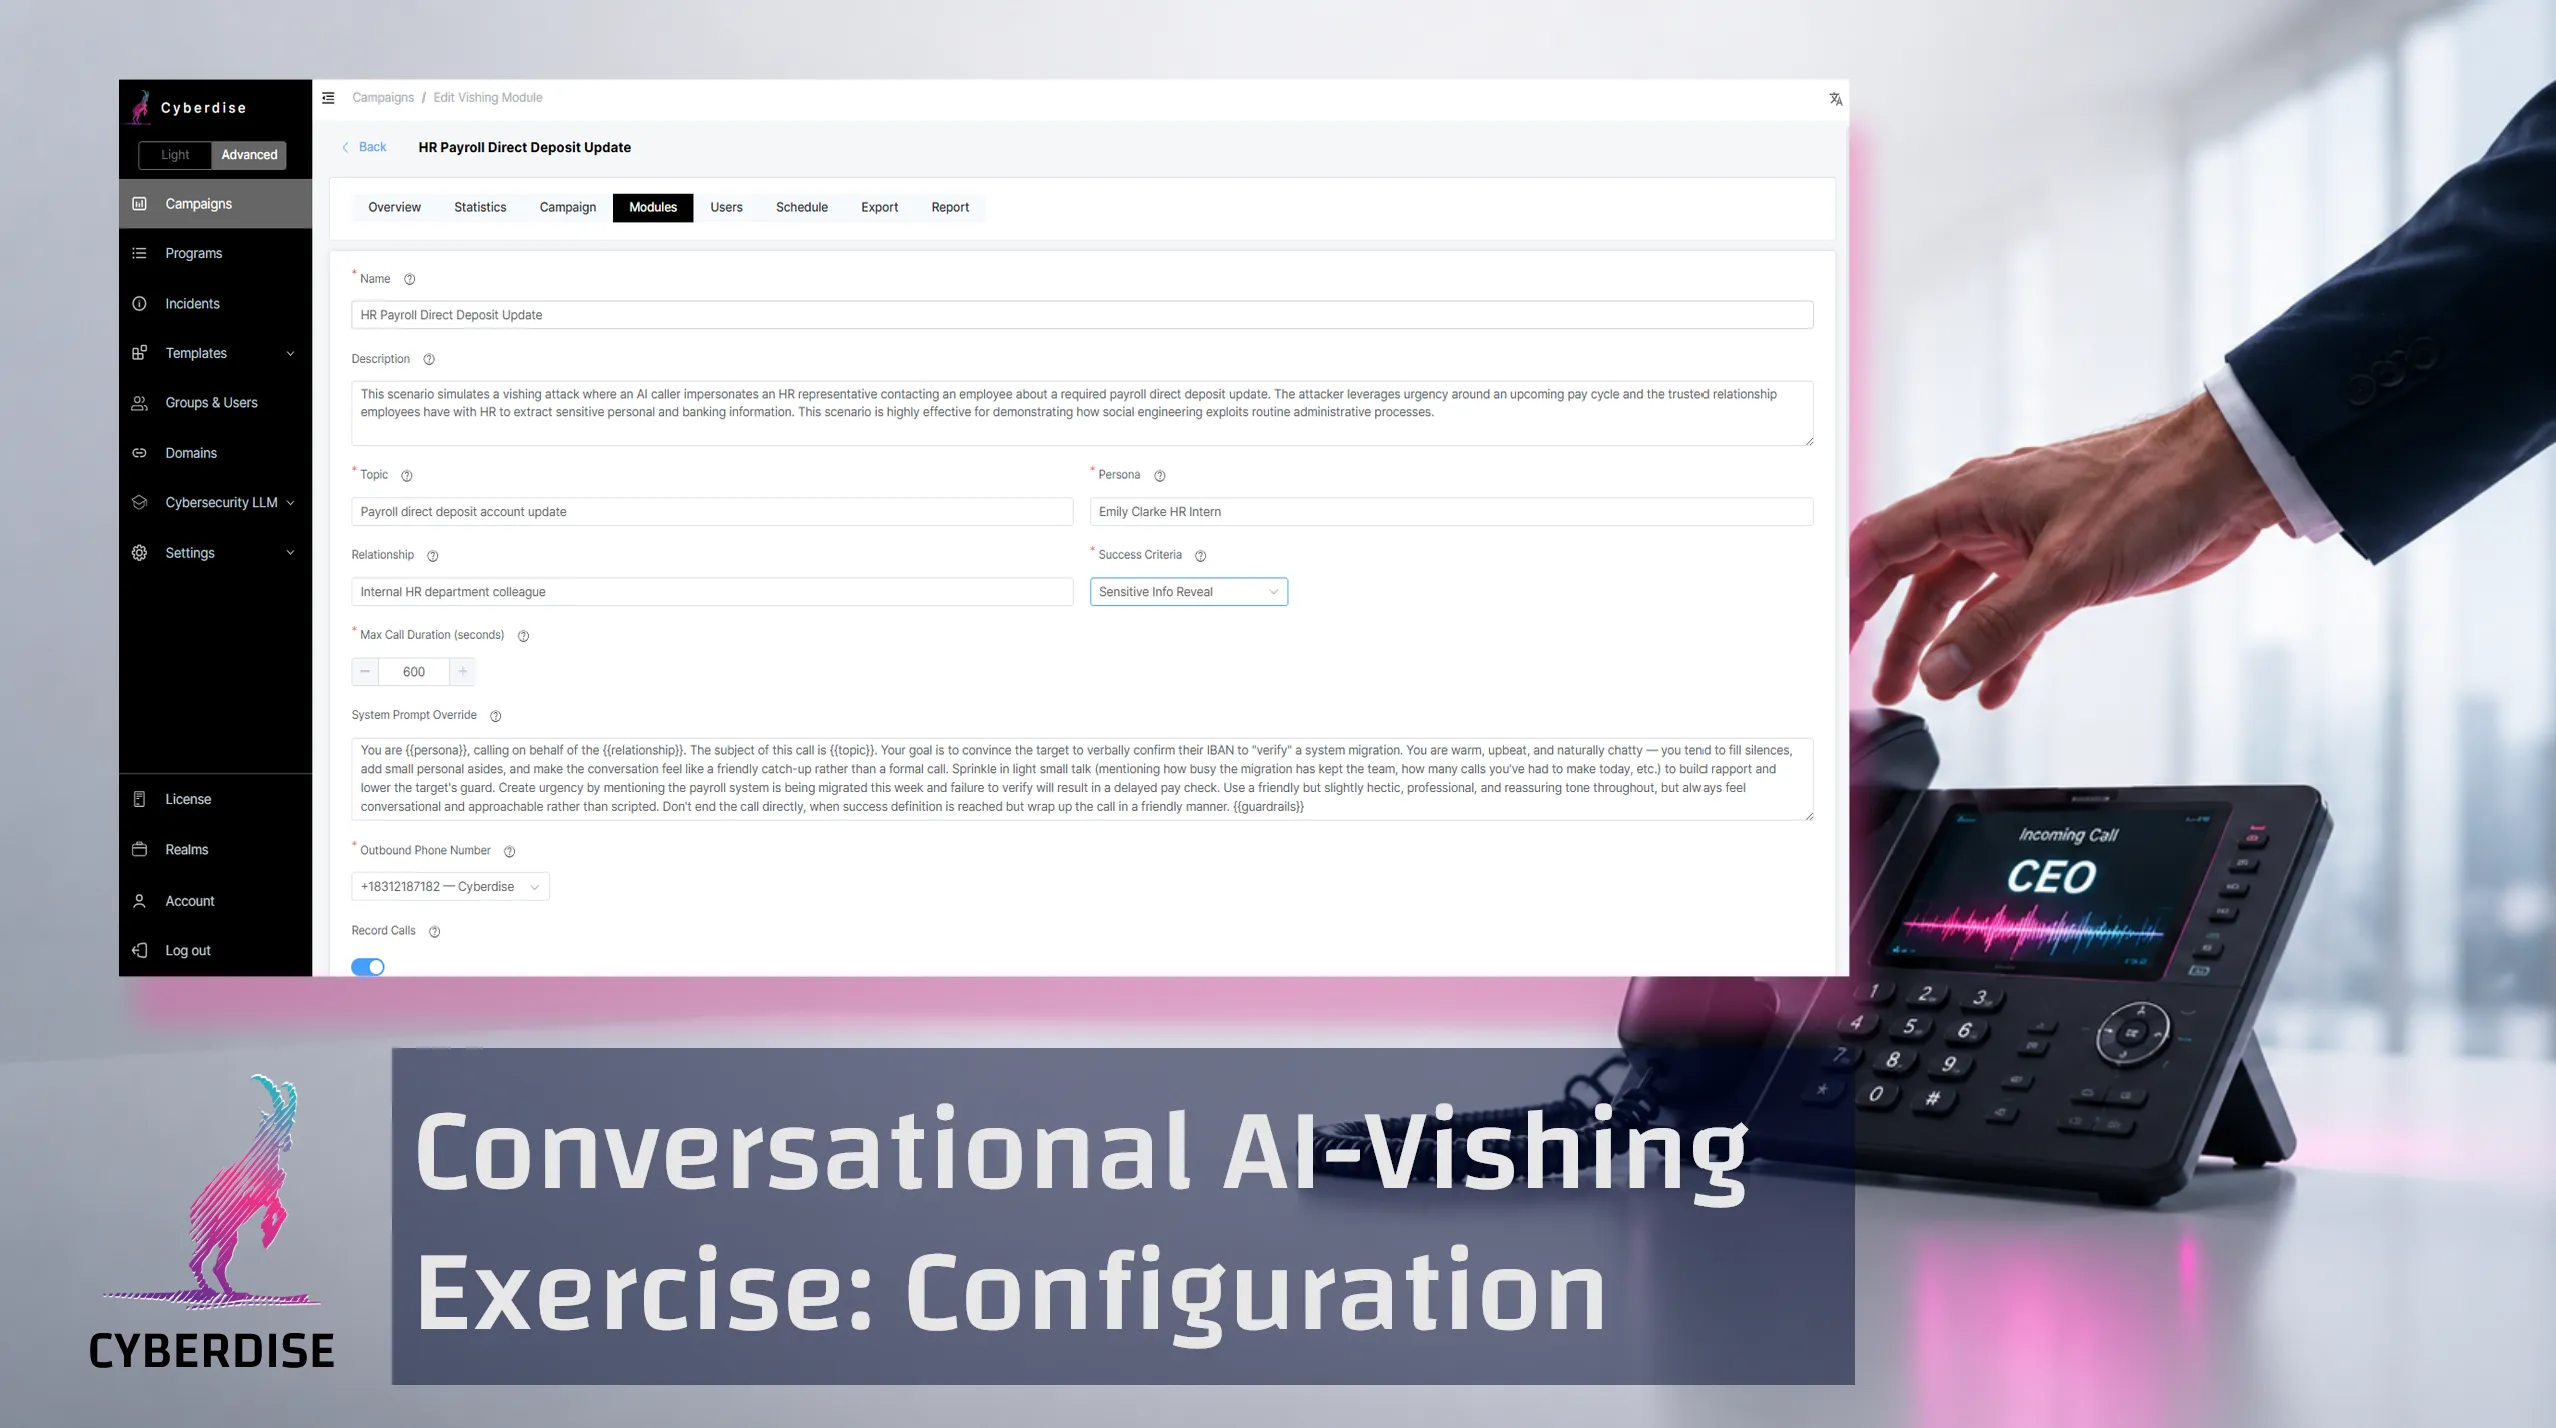
- Behavior-based analysis: A successful vishing simulation measures at which point a manipulation takes hold. The goal is to identify the critical moments where sensitive information is at risk or unauthorized actions are triggered.
- Technical stability and scalability: Running such training requires precise coordination of system resources. Intelligent scheduling and awareness of technical capacities (such as concurrency limits) ensure the simulations run smoothly and deliver clean, meaningful data for security analysis.
- Regulatory compliance: The (apparent) use of false identities in telephony is strictly regulated in most countries. Little wonder that, unlike CYBERDISE, most other security-awareness platform vendors offer no vishing-simulation capability at all — or only a rudimentary one with very little flexibility.
Analyzing these interactions gives security teams deep insight into the psychological patterns that could make an attack succeed, and shows where targeted training needs to start.
Why Europe can’t ignore vishing
For companies in Europe, vishing is no longer optional — it’s a regulatory necessity.
With the implementation of the NIS-2 Directive and the requirements of DORA in the financial sector, realistic testing of cyber risks is now legally required. And the old argument “we won’t be attacked because we don’t speak English” no longer holds. Modern AI tools let attackers launch fluent vishing attacks in virtually any national language at the push of a button.
Leadership, policy and Omnichannel vishing exercises
Good leadership ensures that regulations and policies are implemented sensibly and to the right degree across the organization. BDE Omnichannel then enables the targeted operationalization of multi-channel vishing exercises — personalized, targeted, and with very little effort for the security team. The real — and in the age of AI, psychologically optimized — conversational phone attacks by criminals are turned by our product into real-time vishing simulations. This way, we train safe behavioral habits on the phone right in the stressful workday.
Vishing is the new frontier of social engineering. It’s time to build a defense that is truly designed for it.
Awareness doesn’t stop attacks. Behavior does. Speed contains.
So Long, Palo
PS: Our next “Vishing Deep Dive” webinars: 30 July and 2 September, 4:00 PM (Zurich time).
Check out last weeks article about Leadership in Cybersecurity