Use the Dark Side of the Web to Your Advantage
Thursday 26 November, 16:00 CET, live on Zoom. Palo Stacho shows how dual use OSINT leads to better risk behavior, with Social Engineering Radar, Attack Template Feed and Vulnerability Profiles.

Thirty minutes: a keynote, an interview and your questions.
- 01The keynotePalo Stacho on why most attacks succeed through behavior, and how attackers' own open sources can build better habits. Worked example: the Berlin hack, live in the tool.
- 02The interviewPalo talks to the creator of the Social Engineering Radar, ending with a first look at the radar, Attack Template Feed and Vulnerability Profiles.
- 03Your questionsOpen questions from the audience to both speakers. Bring the attack your team worries about most. Then a short close.
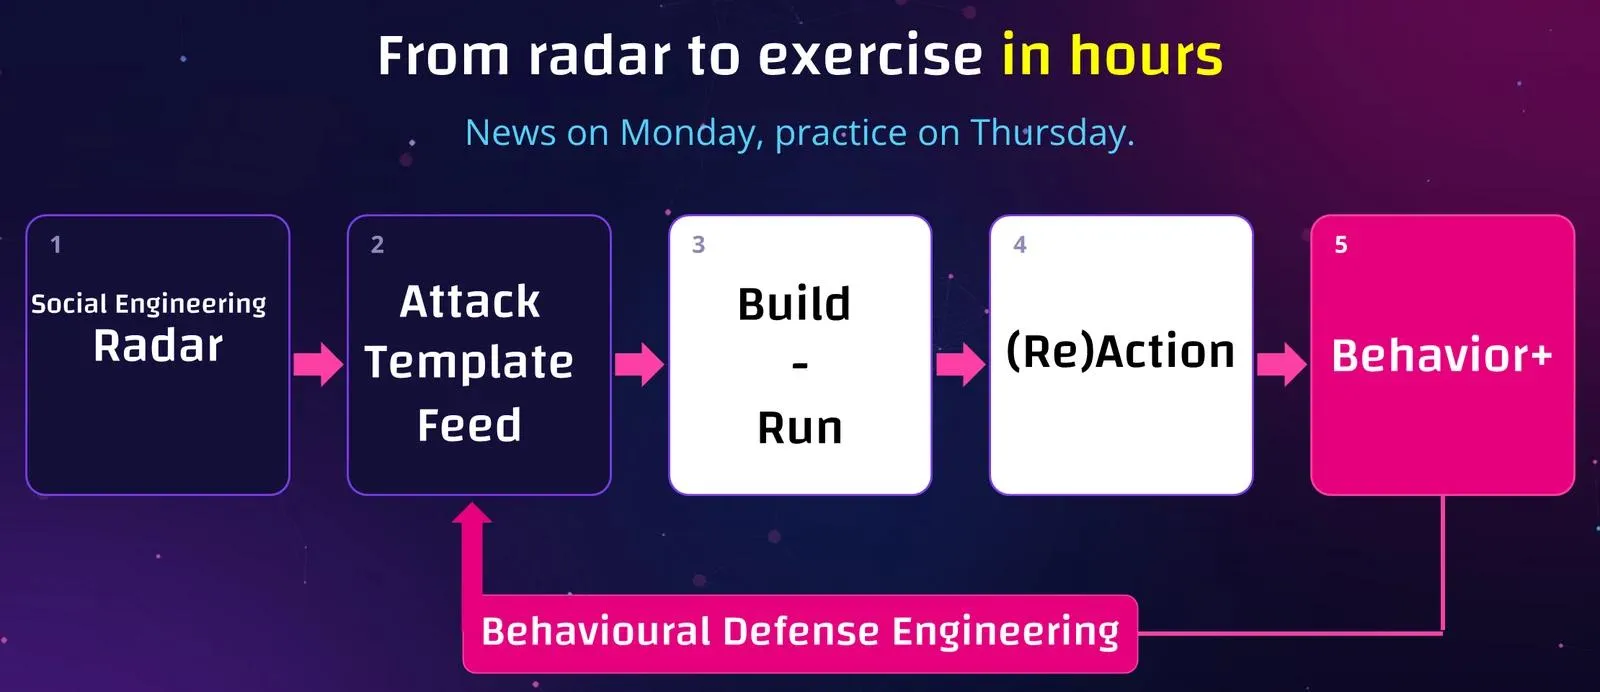
How a headline becomes an exercise
The loop Palo walks through on 26 November. The radar spots an attack, the feed turns it into a template and you run it. Every reaction then shapes the next round.
Vishing deep dive
Sebastian Münster and Joël Waldmüller on voice attacks. Why a voice is harder to doubt than an email, what a cloned one sounds like down a phone line, and how an omnichannel simulation gets built and governed. Thirty eight minutes.
Earlier this year, in full.
The launch of Behavioral Defense Engineering in June, and the customer and partner review in February.
The Behavioral Defense Engineering launch
The session that introduced the category, with the research behind it. Dr. Carlo Pugnetti of the Lucerne School of Business presents the study results, and the rest of the session walks the loop from a reported message to a trained reflex.
- Introduction to Behavioral Defense Engineering
- Study results presented by Dr. Carlo Pugnetti, Lucerne University of Applied Sciences (HSLU)
- A morning with a SOC engineer, as a worked example
- An omnichannel vishing demonstration
- Questions from the floor
Review, news and outlook
What shipped over the previous year, a demonstration of the newer features, and where the platform goes next. Twenty minutes, with questions at the end.
- A review of the year's developments
- A demonstration of several features
- Where the platform goes next
- Questions and a vote on what to build
Do I need to sign up to watch?
Where is the study from the launch session?
What has shipped since the February review?
Where can I see how vishing simulations work?
Watched the sessions? See the same attacks run against your own setup.
A 30-minute demo of the exercises from these recordings, by mail, text or a voice on the phone.