Skip to content
Run it in-house

Everything else is in your stack. Awareness should be too.

Your company runs an identity system, a SOC, a ticket queue and a policy on where data may live. Awareness is usually the one control outside all four, in a vendor portal somebody exports a spreadsheet from once a quarter. Cyberdise runs inside your boundary instead.
Your servers
or your cloud, or ours
Your directory
AD, Entra, LDAP
Your SOC
reports land there
Your model
own LLM or open
An enterprise security architect holding a closed laptop, cut out against the page background
Where it runs

Your data stays where your policy puts it.

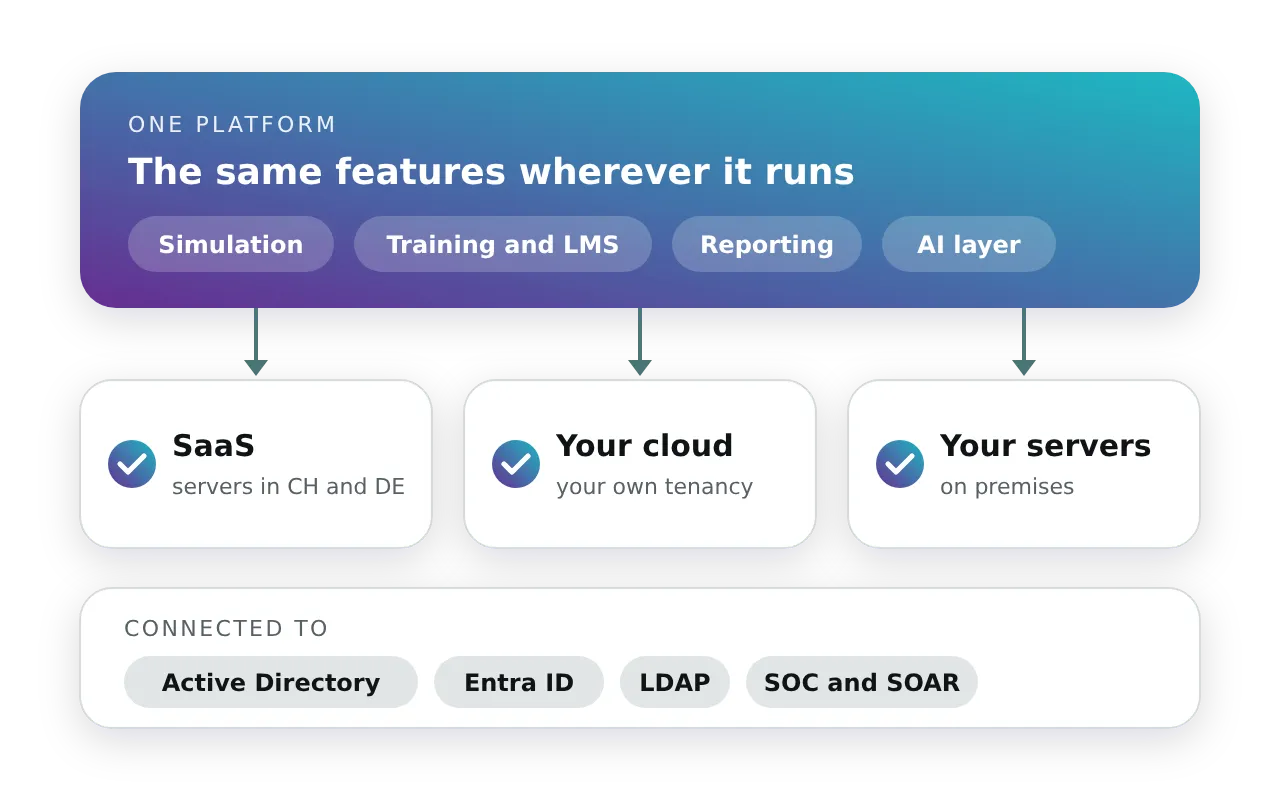
As SaaS, Cyberdise runs in ISO 27001 certified data centers in Switzerland and Germany, which is where your data is stored. Where it must not leave your own walls, run it in your cloud or on your servers. There, it goes through review like any other internal service.

  • Every feature, whether it runs as SaaS, in your cloud or on your servers
  • On premises as a rootless Docker image
  • Runs behind your proxy, even with no direct route to the internet
  • Outbound mail over TLS, and service logs your operators can download
See what the platform does

One platform with the same features, whether Cyberdise runs as SaaS on servers in Switzerland and Germany, in your own cloud or on your own servers, connected to Active Directory, Entra ID, LDAP and your SOC and SOAR
Integration

Plugged into the stack your team already runs.

Cyberdise takes its users from your directories and hands what people report to your SOC. Nobody maintains a second user list.
Several directoriesSync several Active Directory and Entra ID domains plus LDAP, filtered to the people you need.
Self-updating groupsDynamic groups follow rules such as department or location, so joiners and movers land in the right campaigns.
Single sign-onOperators and employees sign in through SAML 2.0 or LDAP, and MFA can be enforced on the User Portal.
Reports become casesRepeat reports of one attack reach your SOC or SOAR as one case, and reported exercises stay out.From report to case
Open APIA documented REST API connects Cyberdise to your SOC and your own tools.
Straight to the inboxIn Microsoft 365, exercises arrive through Microsoft Graph, past the spam filters and with far less allowlisting to set up.
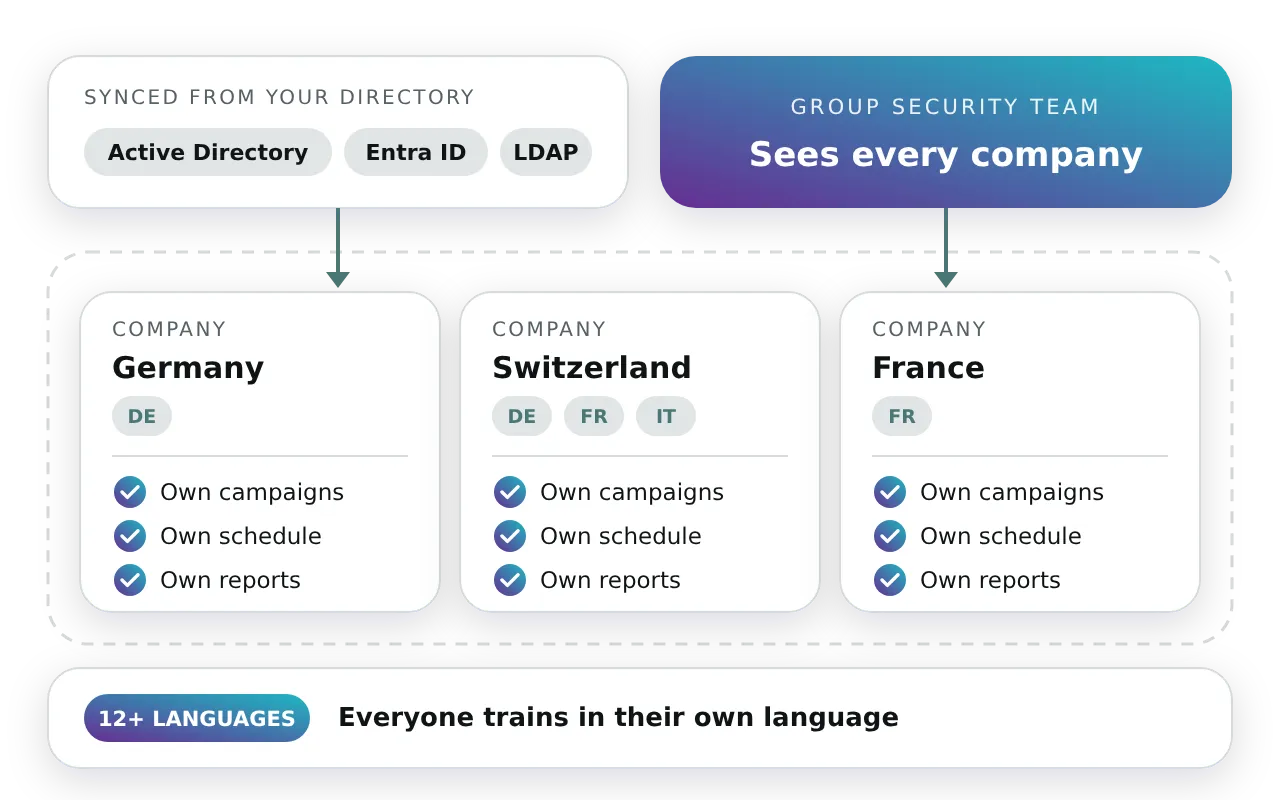
One Cyberdise platform for a group: users sync from Active Directory, Entra ID and LDAP into a separate environment per company, each with its own campaigns, schedule, reports and languages, while the group security team sees every company, with content in 12+ languages
Rollout at scale

Every company runs its own program, and you see all of them.

Each subsidiary gets its own realm, with its own campaigns, domains and reports, and its local operators see only their own. Templates go out in each person's language, so Lyon trains in French and Zurich in German.

  • A separate realm per company, with a group-wide view on top
  • Content in 12+ languages, matched to each person automatically
  • Several Microsoft 365 tenants handled from one realm
  • Onboarding schedules and reminders that run without anyone chasing

See how results roll up

Governance

Ready for your works council and your DPO.

These are the points a works council or data protection officer tends to raise first, and what the platform does about each.

Anonymous by fieldHide names, email addresses or other fields per campaign, and the setting locks once the campaign is saved.
Read-only oversightWorks council members can have their own read-only account and look at the data directly.
Minimal dataA simulation records the interaction and technical details, and form entries only if you switch that on.
Retention you setLeavers are archived with their history, then deleted by hand or after a period you choose.
Your AI modelAI features run on the model you pick, including an open model on your own servers.
AI under your controlAI-built campaigns go out only after an operator approves them.
Getting started

How a rollout begins.

A Cyberdise partner usually runs it with your team. Where no partner is involved yet, Cyberdise supports you directly.

  1. 01ScopeA first call settles your hosting rules, your directories and who will operate the platform.
  2. 02Set upCyberdise guides the installation and the first directory sync, whether it runs as SaaS or on your servers.
  3. 03Brief the works councilShare the anonymization concept and the campaign plan early, before any exercise goes out.
  4. 04BaselineA first exercise in one company or group gives you the number every later result is measured against.
  5. 05Scale outAdd the next companies and languages, then let the schedules run.
The evidence

The number to bring to your board.

~60%less risky clickingafter AI spearphishing exercises, against baseline
4test groupsfrom no intervention to AI spearphishing
539employeesin the study, November 2024 to June 2025
We run KnowBe4 or Microsoft Defender today. Why switch?
Because a click rate only tells you who fell for it. Cyberdise also measures who reported and how fast, scores behavior instead of course completion, and trains people on the attacks that actually reach them. Your SCORM courses come across as they are, so you keep what you've built. Compare it with KnowBe4, or see what Behavioral Defense adds to awareness training.
Will our works council accept it?
It's built for that conversation. Results can be anonymized fully or partially. In Anonymous Mode, the fields you choose to hide, such as names and email addresses, stay hidden everywhere, and the setting locks once the campaign is saved. Your works council can check that for itself. How results and anonymity work
Can it cover every subsidiary and country in the group?
Yes. Give each subsidiary its own realm, with its own campaigns, schedule and reports, and your group team sees across all of them. Courses come in 12+ languages, so every country trains in its own. The platform serves more than 500,000 licensed users.
Where does our data live?
Where your policy says. As SaaS, on servers in Germany or Switzerland. Or in your own cloud or on your own servers, with the same features wherever it runs. Deployment options by edition
Part of our mail still runs on Exchange on premises. Can people report from there?
Yes. The Report-a-Phish Button works in Outlook on Exchange on premises as well as on Microsoft 365, with nothing to register in Azure. See the button
Which AI model does it use?
The one you choose. Cyberdise works with leading commercial models and with open models, including one running on your own servers, so the AI features keep working where data may not leave the building. How the AI fits the platform
Who runs the platform day to day?
A Cyberdise partner, your own team, or both. A partner can run the campaigns and look after an on-premises installation while your security team keeps the decisions. Cyberdise supports you directly during setup. See the partner program
How is pricing worked out for a group?
Every group gets an individual offer, with no hidden fees. It reflects how many people you protect, where the platform runs and how much you want to operate yourself. Get pricing

Plan the rollout for every subsidiary in one call.

A 30-minute demo built around your hosting rules, your directories and the questions your works council will ask.