Practice on the attacks people actually get.
An outdated template library trains people for last year's phishing. Cyberdise builds exercises from the tactics attackers are using now, across email and SMS, in the languages your people work in.
The email at the desk, the text on the way home.
Attackers reach people wherever they happen to be looking, so your exercises should too. Cyberdise runs email and SMS from one place rather than from four tools that don't talk to each other. Texts go out from your own sender number, and in Microsoft 365 the email can land straight in the inbox.
- Email and SMS lures, QR codes included
- Data entry, hyperlink and file scenarios, with file links aimed where you choose
- Double barrel and multi attack campaigns
- Website cloner, landing pages and custom error pages
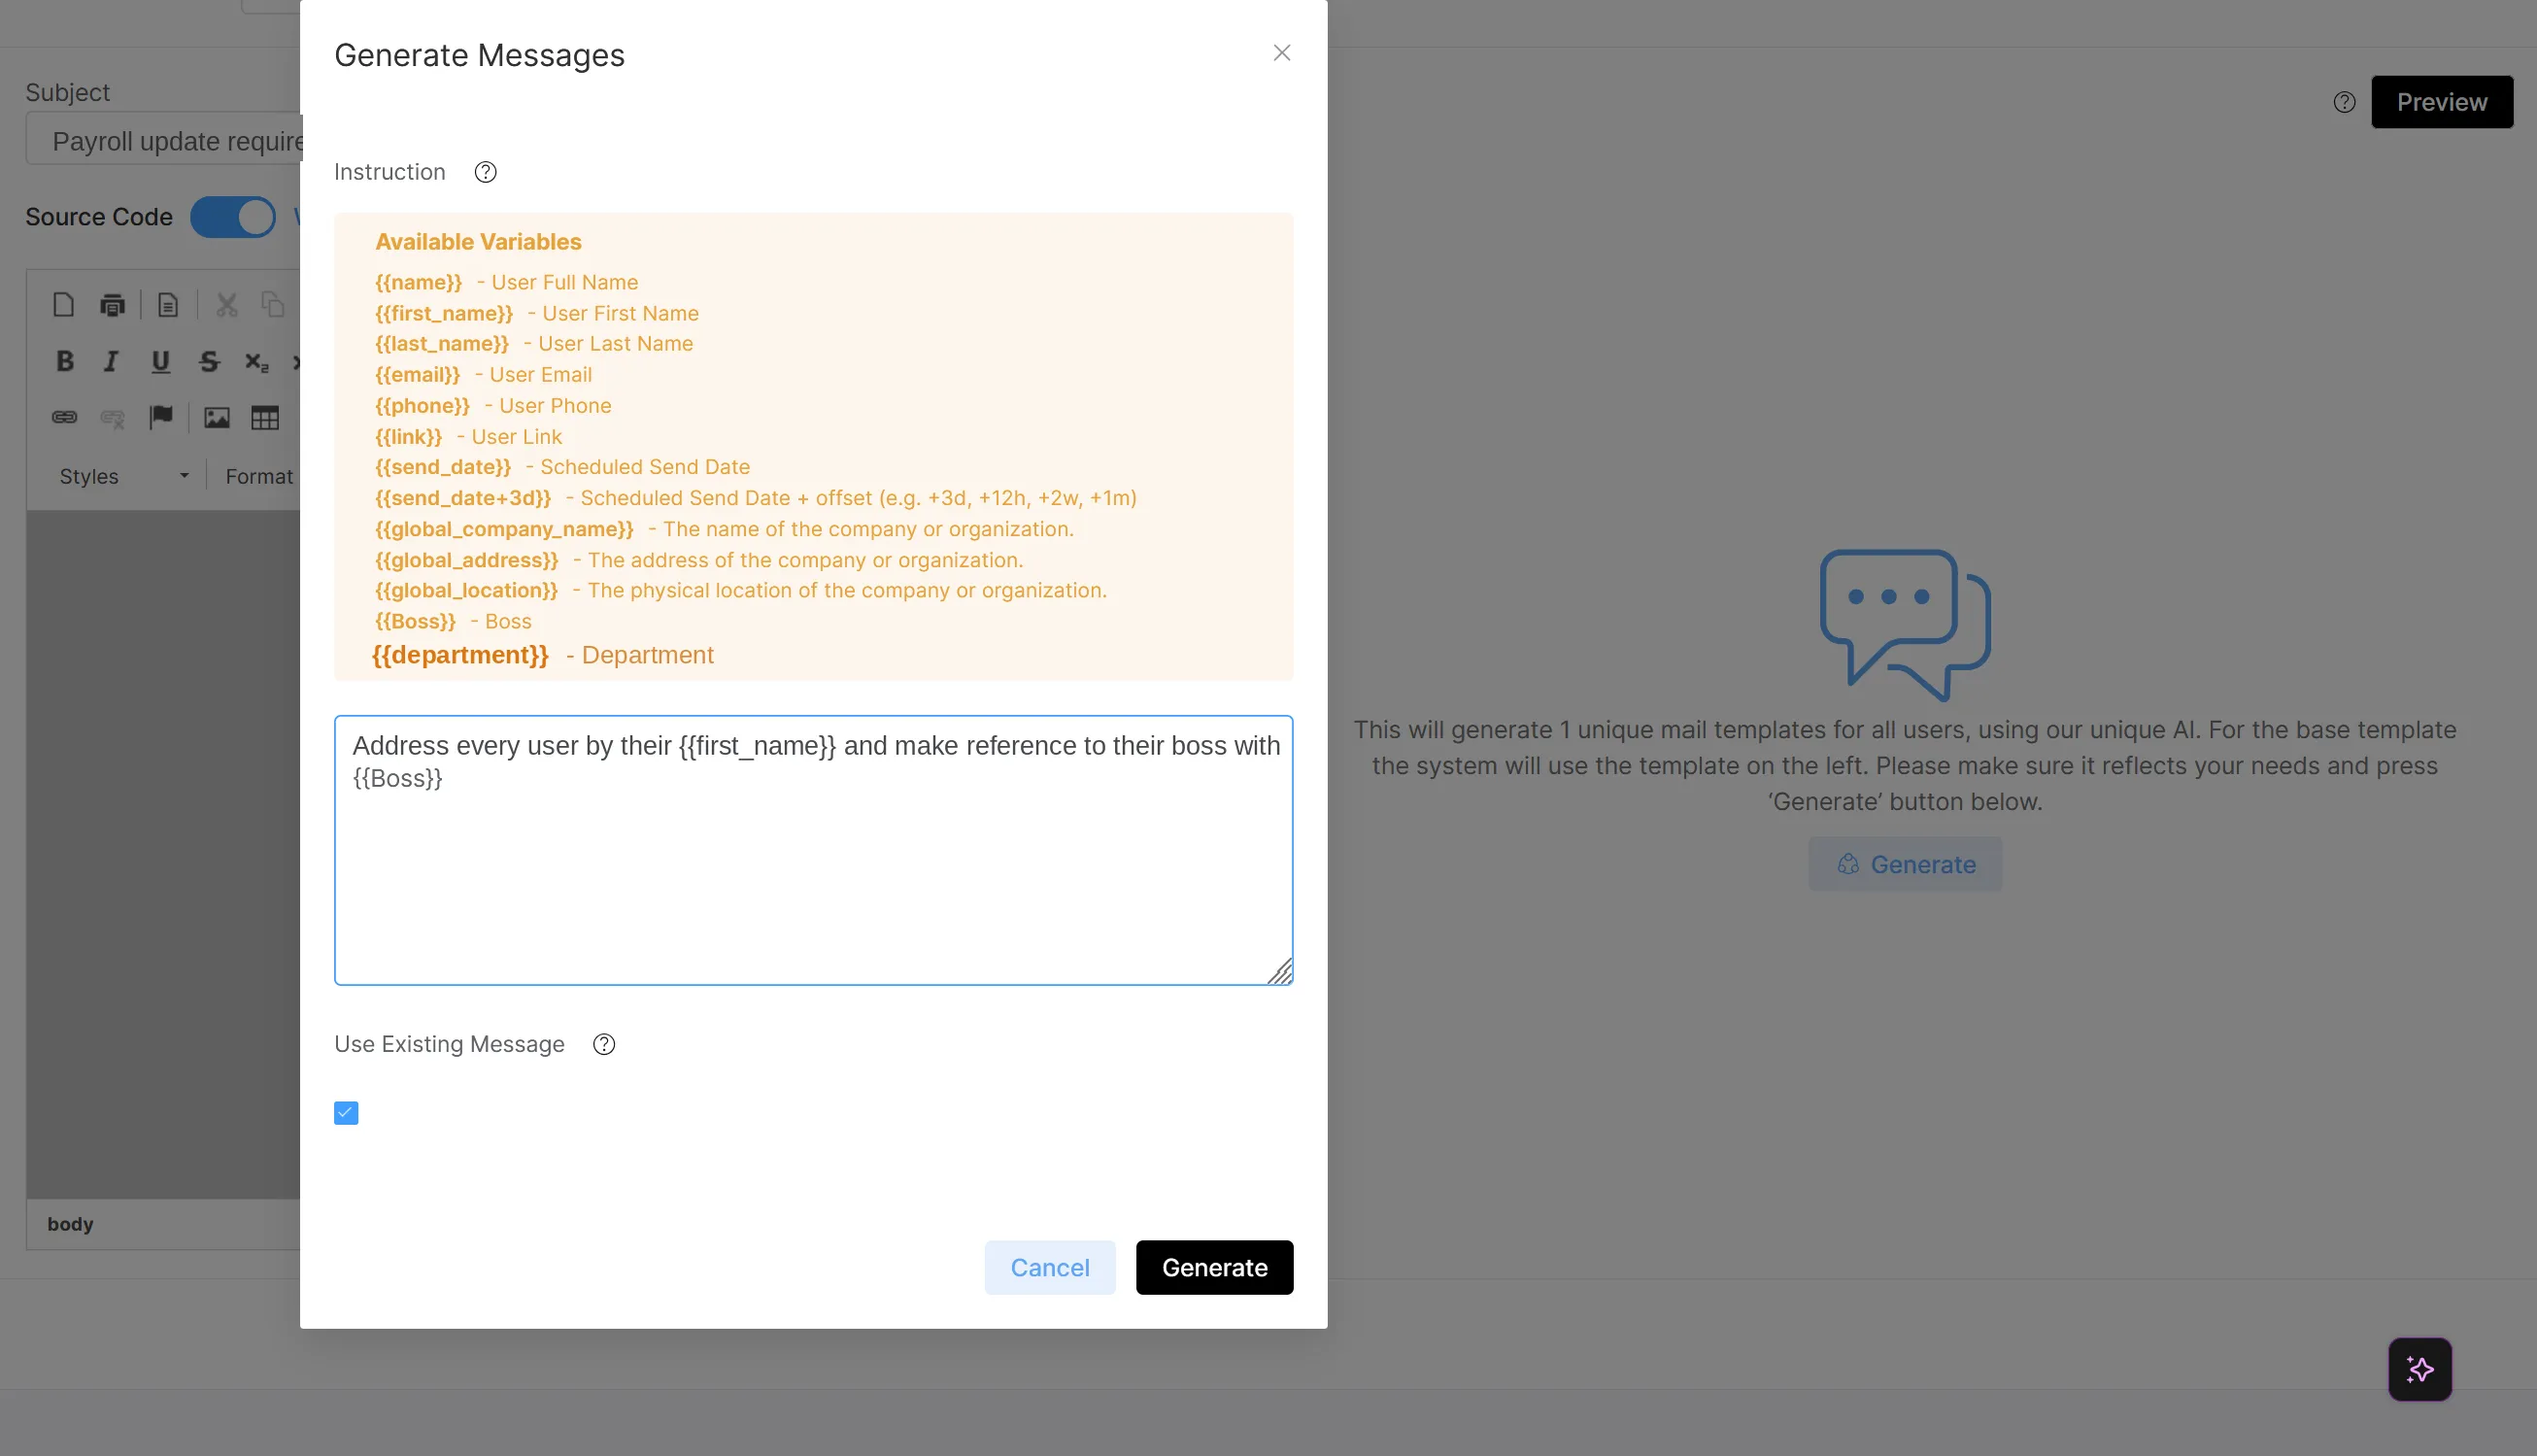
- Custom, gender and AI variables
Exposure changes behavior. Training changes attitude. You need both.
Source: AISP study
Realistic without the manual week.
One template, a message for every recipient.
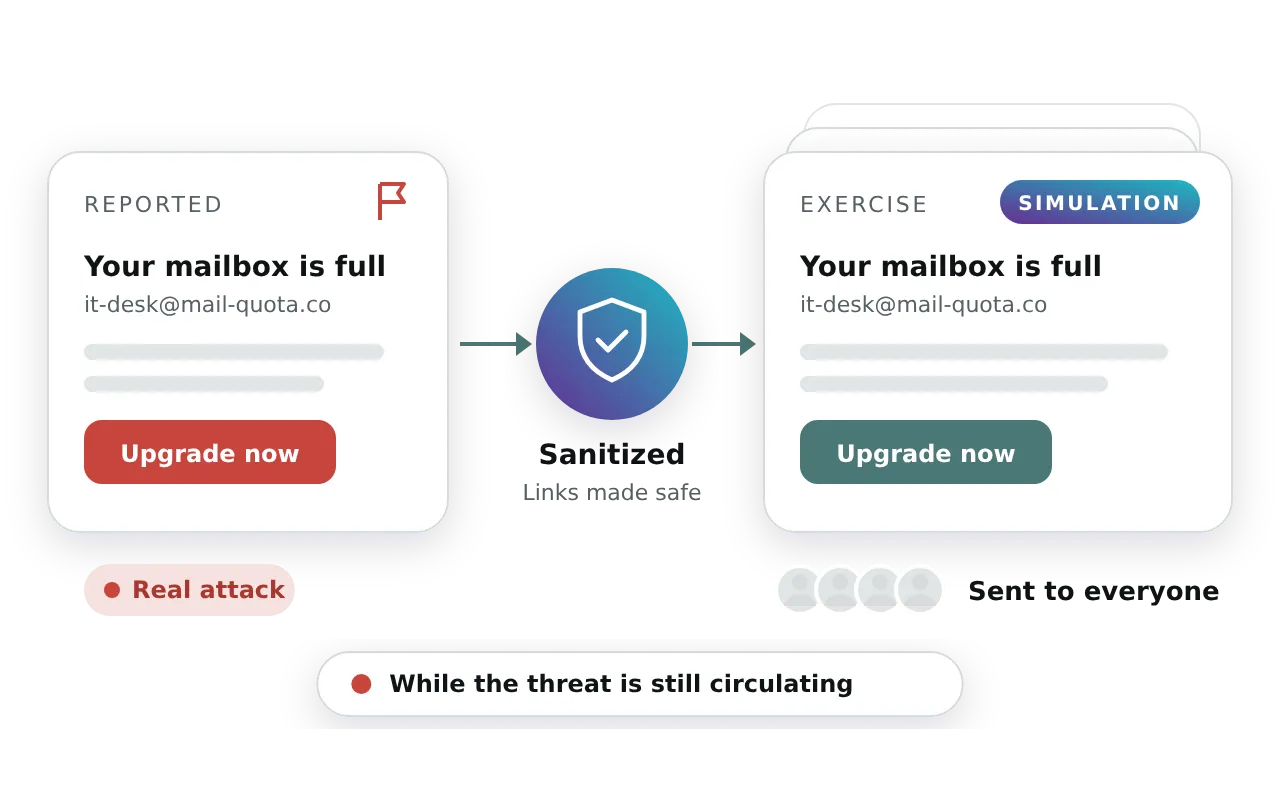
A real attack, turned into everyone's exercise.
When someone reports a genuine phish, it does not have to end as an incident ticket. Cyberdise turns the reported message into a sanitized exercise for the wider organization, while the threat is still circulating. The person who reported it gave the whole company its next lesson.
Spotting the exercise is the start. Reporting it is the point.
Will the exercises get past our spam and phishing filters?
Is there a way past the mail filters in Microsoft 365?
How do SMS exercises work?
Can we run exercises without naming individuals?
Which languages can an exercise run in?
Can we reuse a template in another realm or installation?
Bring a scenario. We build the exercise live on the call.
Bring a real phish your people received and see it become an exercise, with training attached.