Human Defense Month goes to Nuremberg.
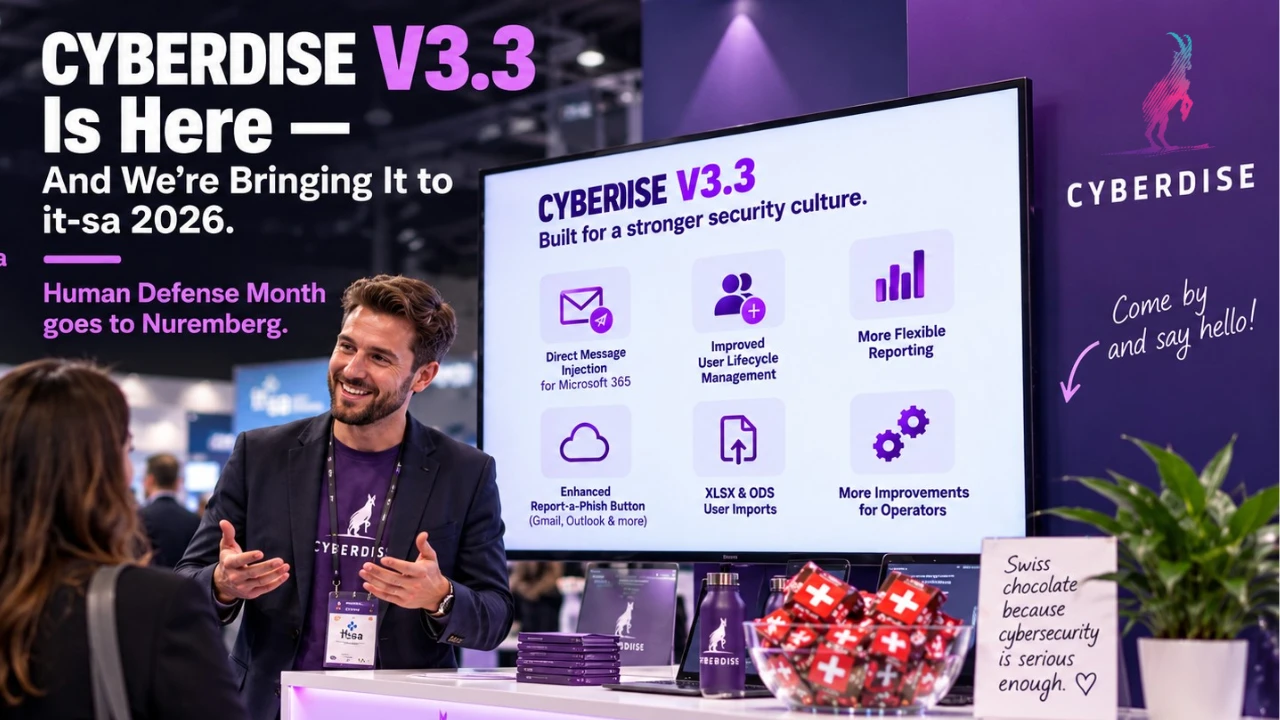
From 27 to 29 October 2026, CYBERDISE will be at it-sa in Nuremberg. You will find us in Hall 7, Booth 301a.
If you are attending, come by and say hello ☺ Palo, Sebastian and Joel are looking forward to meeting customers, partners, awareness professionals and everyone who wants to talk to us, not only about Behavioral Defense Engineering.
And yes, there is another reason to visit: You can pick up your Swiss chocolate bar. 🇨🇭🍫 Because Cybersecurity is serious enough, after all.
What’s new in Cyberdise V3.3
it-sa also marks the launch of CYBERDISE V3.3, our Human Defense Month release.
V3.3 contains quite a few improvements for operators, especially around phishing simulations, reporting, user management and day-to-day administration.
One of the bigger additions is Direct Message Injection for Microsoft 365. CYBERDISE can now deliver simulation messages directly into Microsoft 365 inboxes through the Microsoft Graph API. This improves delivery reliability and can considerably reduce the usual work around SMTP filtering and whitelisting.
We have also improved user lifecycle management. Users who disappear from a connected directory no longer have to disappear together with their historical campaign data: they can now be archived, restored later or permanently deleted according to your retention settings.
Reporting gets more flexible
The CYBERDISE Report-a-Phish Button has received several updates as well.
Gmail and Outlook! Simulation emails and genuine suspicious messages can now follow different reporting routes. Outlook support has been extended to shared mailboxes, group addresses and additional accounts, and the button can also be used in environments without Azure — including on-premises Exchange and other mail setups. Reported messages can also be forwarded in additional formats, including EML attachments, helping preserve the original message for further analysis.
A few more things operators asked for
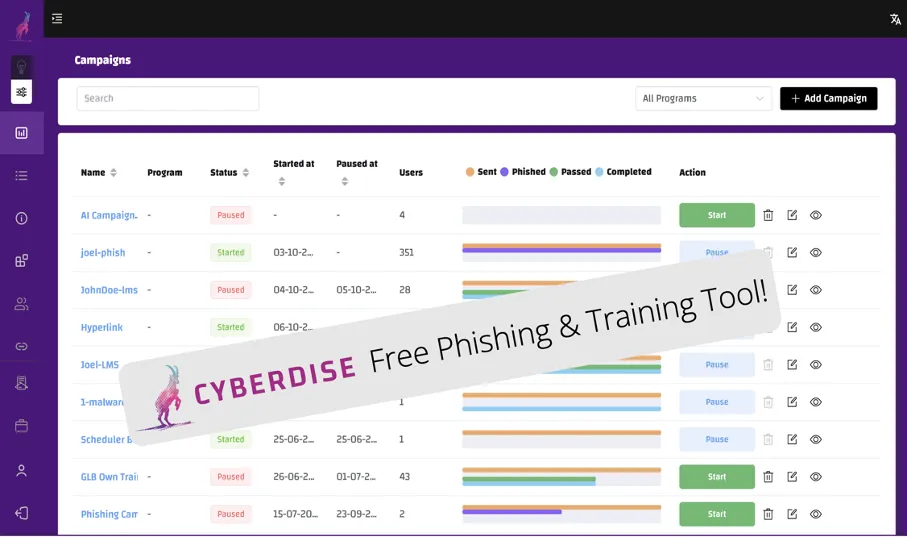
User import: V3.3 also introduces XLSX and ODS user imports with field mapping, validation, cleansing and import previews.
Administration and security: There is improved logging, outbound TLS support, proxy support, stronger user portal access controls and enhanced template import/export — including Cyberdise and SCORM formats with their associated components and language versions.
Funny stuff: And because V3.3 is also our Human Defense Month release, we may have hidden one or two things inside that are considerably less serious. Have a look around in your own CYBERDISE instance ;-)
See Cyberdise V3.3 live at it-sa 2026
If you want to see V3.3 in action, discuss your own awareness or Behavioral Defense Engineering programme, or simply collect some Swiss chocolate, Palo, Sebastian and Joel are looking forward to seeing you there:
Read the complete CYBERDISE V3.3 Release Notes
And if you have not explored Human Defense Month yet: Explore the free Human Defense Month 2026 Community Kit
Business is serious enough, let’s have some fun together this month. :-)
So long, Palo