I read the new SANS Security Awareness & Culture Report with a slightly unusual perspective: I manufacture security awareness software. And the finding that stayed with me is about security awareness team size — not about tooling at all.
So, obviously, I should be looking for statistics that prove companies need more technology, more automation and preferably more software. Because most people in the industry tell everyone that awareness is really simple and happens automatically. But that is NOT what stuck with me.
Some findings strongly confirm where I believe our industry needs to go. Others challenge the way awareness vendors, and including me, tend to think. And at least one conclusion in the report I fundamentally disagree with.
Here are my eight takeaways.
A good tool gives a good team leverage, but it doesn’t replace the team.
How many people an awareness programme needs
1. You cannot buy your way out of an understaffed awareness program
This may be the most uncomfortable finding for software vendors.
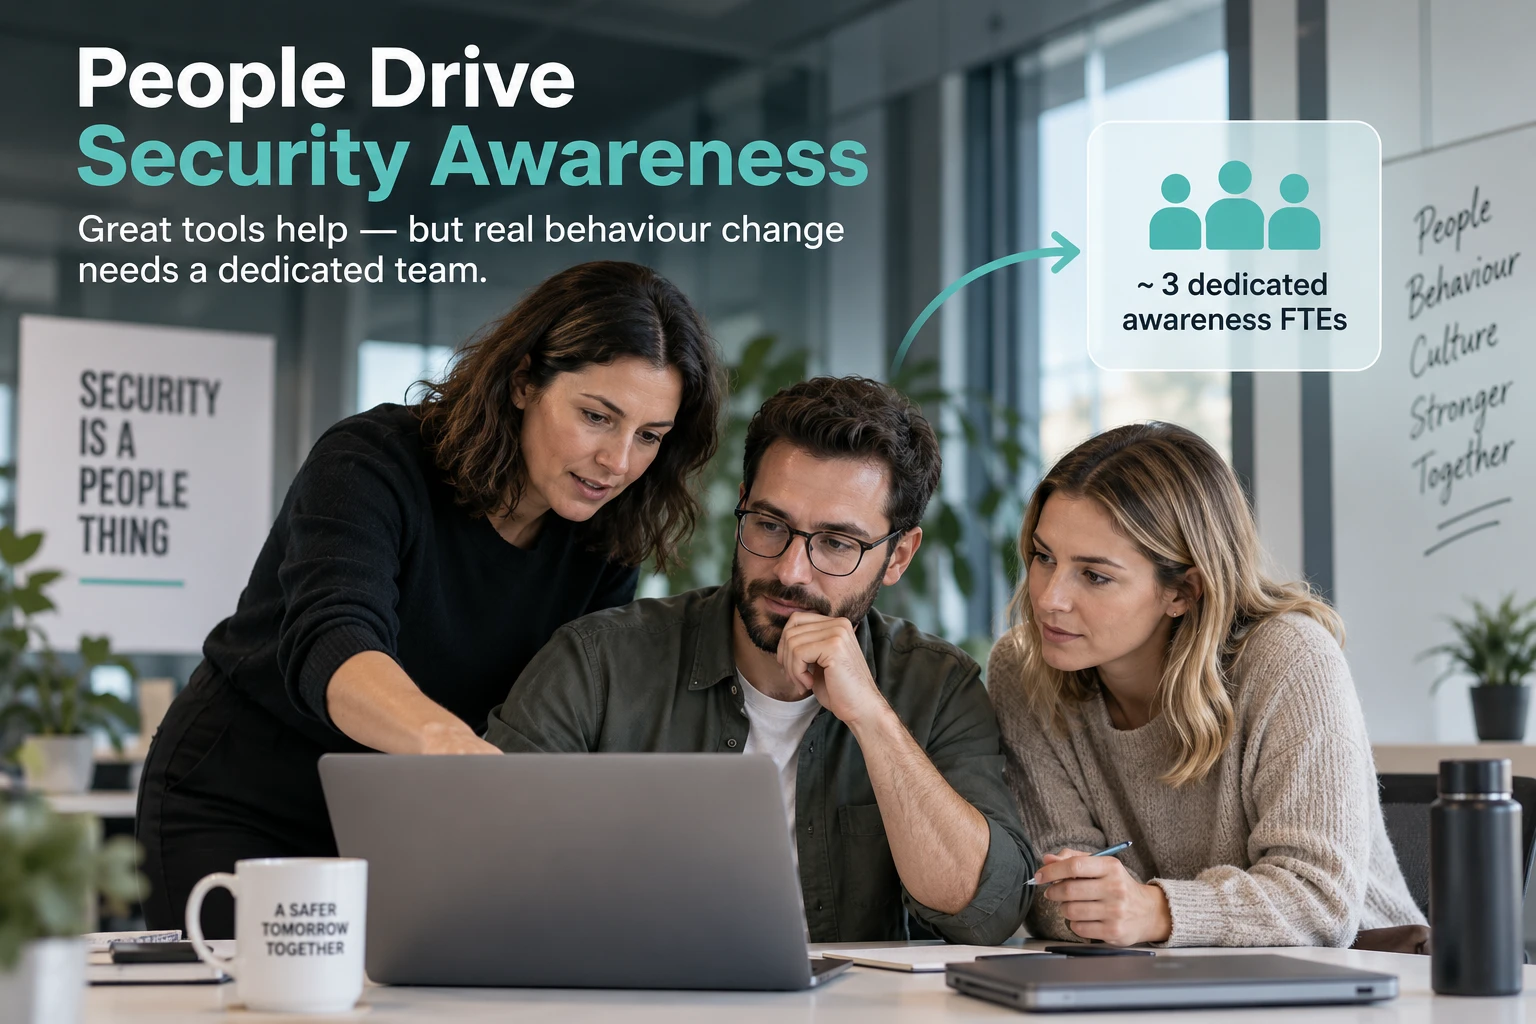
SANS finds that organisations effectively changing workforce behaviour have around three dedicated awareness FTEs. Moving from behaviour change to security culture requires, on average, 4.3 dedicated people.
Think about that.
We vendors like to explain how much work our platforms automate. And they do it a lot. But technology doesn’t build relationships with HR, understand employees, convince management, define the right behaviours or establish trust. And full-service solutions are unable to capture the true context and its nuances in campaigns, emails, and training sessions.
A good tool gives a good team leverage, but it doesn’t replace the team.
Two details in the report make this harder to argue with. SANS counts someone as an FTE only if they spend 75% or more of their time on security awareness and culture — so this is not a matter of adding the work to three people’s existing jobs. And the numbers come attached to timeframes: organisations changing behaviour at scale needed three to five years, embedding culture took five to ten, and the most mature programmes ran more than six dedicated FTEs for more than a decade. Security awareness team size and programme age were the two variables that predicted maturity most strongly.
2. Your security-team composition is probably wrong
SANS offers another number I think every CISO should look at: as a starting point, have one human-focused security professional for every ten technical security professionals.
I like this metric because it exposes an investment imbalance. Companies spend enormous amounts securing endpoints, identities, networks, applications and cloud environments. But attackers increasingly target the person sitting in front of them (well, they always did, right?)
Human defense cannot remain the small awareness corner somewhere next to the “real” security team. It is PART OF THE SECURITY team — which is the same argument we made when we asked why the human layer belongs in your security stack.
Where the report stops short
3. We talk endlessly about security culture — and where are the values?
This was one of my biggest question marks. SANS puts security culture at the very top of its maturity model. Mature organisations are described as places where employees believe in, support and prioritise security in their daily activities.
Good.
But I miss something fundamental: values.
You cannot seriously discuss organisational culture without asking which values create that culture. Do we value openness when someone makes a mistake? Responsibility? Judgement? Reporting early rather than hiding an incident? Helping a colleague? Germans call this ‘Fehlerkultur’.
If we want security culture, those questions deserve much more attention.
4. SANS and its respondents are still underestimating what AI can do for awareness
Here I disagree with the report, because it stops too early.
To be fair, SANS is very positive about AI. It covers content creation, communication, personalisation, data analysis, assessments, program planning, policies and even business cases. But this still looks at AI largely as an assistant to the awareness professional.
The bigger change is AI becoming part of the awareness machinery itself.
If you really want to run proper awareness campaigns with high personalization instead of standardized stuff: Why manually design every campaign when AI can help prompt and generate it? Why stop at personalised training when OSINT can support realistic deepfake or social-engineering exercises? Why not dynamically adapt simulations to roles, languages, attack channels and observed behaviour?
AI can do much more than create prettier awareness content.
What the awareness role really is — and what it pays
5. Security awareness isn’t really a tech job
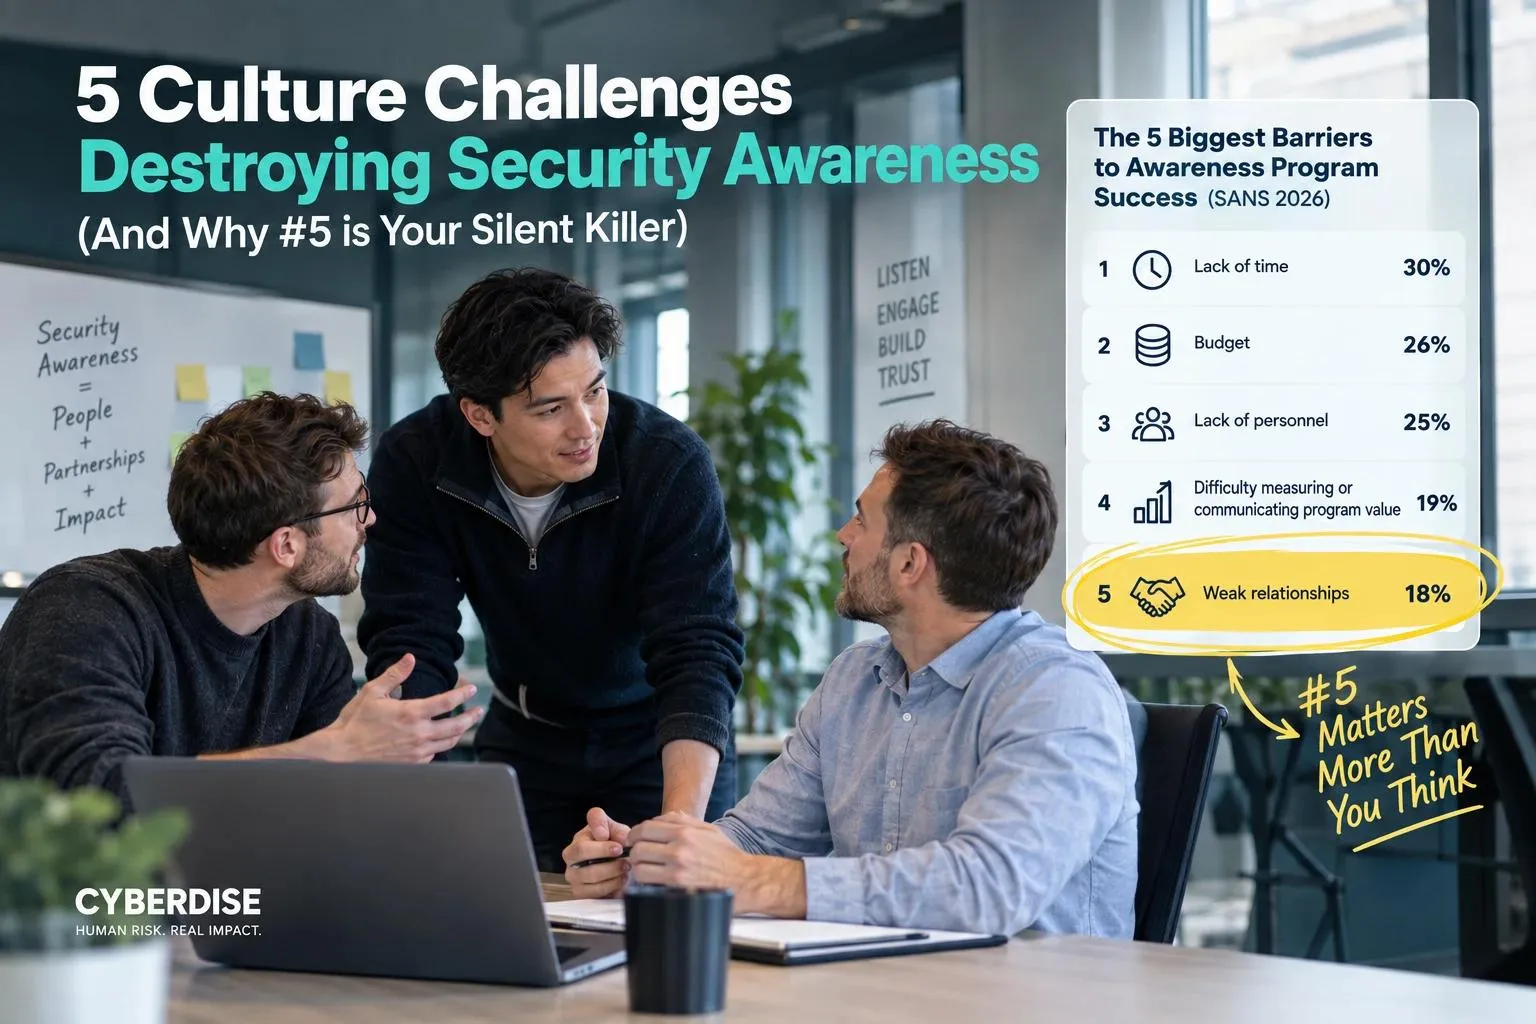
And that’s a good thing ☺ One of my favourite parts of the report is its advice to awareness professionals: think like a marketer.
SANS goes even further in the qualitative section, describing the role as neither primarily a training job nor a technical job, but a behaviour-change role operating in a security context. Exactly! Because the best awareness professional does not necessarily know the most about firewalls.
They understand people, communication, motivation, behaviour, marketing, etc. And they know enough about cybersecurity to connect all of this to real risk. In other words: we may need fewer technical nerds — and more bridge-builders.
6. European awareness professionals earn around $107K. Only?
The report puts the European average at roughly $107,000 per year (around €92K). The global average is $123,624.
This number surprised me, not because it seems low to me in absolute terms. But because of what we increasingly expect from these people. They should understand cybersecurity, human behaviour, risk, communication, marketing, AI, (people, stakeholder, project, etc) – management, analytics and metrics, organisational change. And ideally build relationships between employees, leadership and the SOC.
My perception from the market is that good people combining those capabilities are harder to find. I also think they are more valuable than this average suggests.
What actually changes behaviour — and who becomes part of the defense
7. Y-E-S: simulation matters
This part made me smile. When SANS asked practitioners about their most effective approaches to shifting security behaviour, realistic simulations featured prominently. Successful programs used role-based scenarios, immediate feedback and short learning interventions tied directly to what the employee had just experienced.
That is the critical difference. Knowing what phishing is is not the same as recognising one under pressure. Knowing that suspicious messages should be reported is not the same as actually reporting one quickly during an attack.
It’s not the first time you read this from me: You cannot train behaviour with knowledge alone. You need to exercise the behaviour. We have written about this split before — training shapes attitude, simulation shapes behaviour, and the combination is what holds.
8. Employees are finally becoming part of the solution
Perhaps the most important change in the whole report appears in the qualitative responses.
Across more than 4,500 answers, SANS says one common theme emerged: “people are assets, not liabilities.” The traditional weakest-link narrative is explicitly challenged.
I couldn’t agree more. Fear, punishment and negative style ‘gotcha’ phishing undermine trust. SANS found exactly that: punitive simulations can cause employees to disengage or hide mistakes, while transparency and positive reinforcement work much better. The employee should not be treated as the vulnerability we somehow need to totally control.
They can recognise. They can react. They can report, and their report can become one of the earliest security signals your SOC receives.
That, to me, is the bigger message hidden inside the 2026 SANS report.
Security awareness is slowly moving away from teaching people about security and towards making people an active part of the defense.
We call that Behavioral Defense Engineering (BDE).
We make the human part of the solution, not part of the problem.
SANS Institute, SANS 2026 Security Awareness & Culture Report, 2026 — based on responses from more than 1,700 security awareness practitioners worldwide, including more than 4,500 answers to five open-ended questions. Download the report from SANS.